Latest: Digital For Tech News Click Here


Showing posts with label Hackers. Show all posts

Thursday, 1 May 2014

Hackers Targeted Carlson Hotel in Minnetonka

0 comments


Carlson hotel in Minnetonka has launched its hotel's rewards point system called "Club Carlson Gold Points " , Recently hackers compromised into its security. According to the Hotel Officials , About $35,000 of the worth of rewards of 650 customers has been stolen by hackers.

The company noticed irregular transaction to a club members accounts 12 days ago. Company says that when they noticed the transactions , they immediately freeze the accounts.

All of the members who have been affected and have been contacted and their stolen rewards has been replaced. The company is urging the members which had access to Club Carlson's account to check their balance and change their passwords.

The accounts didn't contained any financial information , it only included the addresses of the members and their email addresses according to the company as they are saying. This case is still under investigation.
Continue reading →

Monday, 21 April 2014

Connecticut under cyber attack , Hackers shutdown power grid station

0 comments


Security challenges are constantly evolving and "becoming more sophisticated and nefarious" and the ability of utilities to detect and stop penetration must constantly improve, the Public Utilities Regulatory Authority said in its report to Gov. Dannel P. Malloy, report about the hack of Connecticut.

Electric, natural gas and major water companies and regional distribution systems in Connecticut have been penetrated by hackers and other cyber attackers, but defenses have prevented interruption.
The report, required as part of legislation enacted last year, said the region's Massachusetts-based grid operator, ISO-New England, has "more sophisticated" cyber defenses than utilities do.

"ISO-NE is constantly being probed, as are all of New England's utilities, many of which have been compromised or penetrated in the past," the report said. "ISO-NE's strength, therefore, depends on both its own cyber defense capabilities and those of each of the utilities with which it works."
The report did not identify the utilities that were compromised or say how. ISO said in a statement that it wouldn't elaborate publicly on security details.

Weaker utilities in the region need to be monitored because failure in one utility could affect the resilience of the region's system, the report said.

Referring to what utilities and water companies can do to protect against threats from workers inside their companies, the report said personnel security requires a balance "between prudence and overkill.".

Regulators said a traditional reliance on employees with no criminal background is inadequate. "Terrorists, hackers and spies rarely have damaging, discoverable police records," the report said.
The report warned that compromise could come from employees with ideological or other personal identifications that "motivate disruptive behavior." And it said it's virtually impossible to thoroughly vet all employees with potential contact to operations, including maintenance, food services and other vendors.

Regulators compared the two destructive storms of 2011 and Superstorm Sandy in 2012, both of which knocked out power to much of Connecticut, with cyber-attacks that threaten utilities' reliability and resilience.

Regulators hinted at higher costs to beef up security. The possibility of cyber-attacks raises the issue of "appropriateness of cost for cyber defense," the report said.

Continue reading →

Three Hackers Arrested in South Korea, Self-Described as ‘Anonymous’

0 comments


Latest arrest in South Korea is against cyber-attack.

The Chosun Ilbo reports that two teenagers and a university student were recently arrested for threatening to launch cyber attacks on the South Korean government on April 14, 2014.

The three, surnamed Kang, 17, Bae, 14, and Woo, 23, posted a YouTube video on March 21, 2014, stating, "To the Government of South Korea. We are watching you, and We Expect for the changes of the Korean Government. ... This is the LAST WARNING MESSAGE for Korean Government. In April 14th 2014, Expect Our Revolution and You CAN'T STOP US!!"

According to the police, the threat was a prank.

While Kang and Bae had met via Anonymous' Facebook and Twitter pages and Kang claimed to be a member of Anonymous, none of the three appears to have any hacking skills. "Police became suspicious when Anonymous denied the attack plans," the Chosun Ilbo reports.

These three have been charged with threatening to launch cyber attacks against the Korean government.
Continue reading →

Pakistani hackers hacked BJP Junagadh website

0 comments

"This is purely an attempt to get votes by playing the communal card ahead of the election" said by Gujarat Pradesh Congress Committee's President Arjun Modhwadia. These were his comments when news came about the hacking of BJP Junagadh website.


According to the officials of BJP the website shows some anti-view of party which may harm the good image of party in their voters. Some resources say this is done by a Pakistani Hacker “Sniper haxXx” who is been responsible for many hacked websites of India in recent past.


Sniper haxXx is been hacking many websites specially which were anti-Pak but this time they have hacked a political party’s website just to break their GOOD image so that they may not get good votes and can get no victory in elections – this is what BJP believes.


Police has reported the complaint about this and has started search to find the responsible people of this hack. Now BJP has to wait for some time no one can say for how long to get this case be resolved.


Some defacement-mirror of website shows, the hack appears to have taken place in February.  It is unclear whether these local reports referring this incident or the website got defaced again. The comments of opposite party’s presidents can never be taken as for granted, you never know what political parties can do.
Continue reading →

Hackers Stole 200,000 South Korean Credit Cards Data

0 comments


Hackers stole the personal information of about 200,000 South Korean credit card users, making some fake credit cards and rack up fraudulent charges about $115,400.

The Financial Supervisory Service said that several suspects had late last year hacked into firm card managing payment processing terminals and extracted datas such as numbers, expiry dates and passwords for a point-amassing loyalty card.

The suspects exploit that some of the users had been using the same PIN numbers and or passwords for the both credit cards and loyalty card to create fake card to charge items earlier this year.

South Korean Police , the one which are investigating have so far identified 268 different cases of wrongful chatges. The leaked information , including cards issues by the biggest cards firm, Shinhan Card which didn't included pin numbers or passwords .

The hacking of the credit cards almost destroys credit cards owner's life as the hackers card things from the money of other persons but carders are the most wanted people in the list of agencies as every step is dangerous for carders.

Some even card things for others like other people buy hacked credit cards like 200,000 credit cards were hacked so same like this people buy hacked credit cards and provide to carder so they can card anything that they wish to have but this thing is wrong that you buy things for your ownself on others money.
Continue reading →

Tuesday, 15 April 2014

How Heartbleed Bug Exposes Your Passwords to Hackers

0 comments
How Heartbleed bug Exposes Your Passwords to HackersAre you safe from the critical bug Heartbleed?? OpenSSL- the encryption technology used by millions of websites to encrypt the communication and is also used to protect our sensitive data such as e-mails, passwords or banking information. But a tiny, but most critical flaw called "Heartbleed" in the widely used OpenSSL opened doors for the cyber criminals to extract sensitive data from the system memory.SSL and TLS are known to provide communication security and privacy over the Internet for applications such as websites, email, instant messaging (IM), including some virtual private networks (VPNs).Heartbleed is a critical bug (CVE-2014-0160) is in the popular OpenSSL cryptographic software library, that actually resides in the OpenSSL's implementation of the TLS (transport layer security protocols) and DTLS (Datagram TLS) heartbeat extension (RFC6520).This bug was independently discovered by a team of security engineers (Riku, Antti and Matti) at Codenomicon, while improving the SafeGuard feature in Codenomicon's Defensics security testing tools, and Neel Mehta of Google Security, who first reported it to the OpenSSL team.Software vulnerabilities may come and go, but this bug is more critical as it has left the large number of private keys and other secrets exposed to the Internet. The heartbleed bug can reveal the contents of a server's memory, where the most sensitive data is stored, including the private data such as usernames, passwords, and credit card numbers. This could allow attackers to retrieve private keys and ultimately decrypt the server's encrypted traffic or even impersonate the server.
“The Heartbleed bug allows anyone on the Internet to read the memory of the systems protected by the vulnerable versions of the OpenSSL software. This compromises the secret keys used to identify the service providers and to encrypt the traffic, the names and passwords of the users and the actual content. This allows attackers to eavesdrop on communications, steal data directly from the services and users and to impersonate services and users.”
OpenSSL is most widely used cryptographic library for Apache and nginx Web servers, which handles a service of Transport Layer Security (TLS) called Heartbeat, an extension added to TLS in 2012. The combined market share of just those two, Apache and nginx, out of the active sites on the Internet is over 66% according to Netcraft's April 2014 Web Server Survey.Moreover, OpenSSL is used to protect email servers (SMTP, POP and IMAP protocols), chat servers (XMPP protocol), virtual private networks (SSL VPNs), network appliances and wide variety of client side software. Many large consumer sites are also saved by their conservative choice of SSL/TLS termination equipment and software. OpenSSL is also very popular in client software and somewhat popular in networked appliances which have most inertia in getting updates.

Security researcher 'Robert Graham' scanned the Internet and found that more than 600,000 servers are vulnerable to heartbleed flaw, including Yahoo.com, imgur.com, flickr.com, hidemyass.com. [List]

Because of Heartbleed bug, the Canada Revenue Agency was forced to shut down its electronic tax collection service yesterday and apparently, World's biggest audio platform SoundCloud also logged out its users for fixing this flaw.How Heartbleed bug Exposes Your Passwords to HackersYahoo, which has more than 800 million users around the world, also has been exposed by the bug.
How Heartbleed bug Exposes Your Passwords to Hackers
HOW HEARTBLEED WORKS?It is not a problem with the TLS/SSL technologies that encrypt the Internet, neither with how OpenSSL works. It is just a dumb coding mistake.

Using Heartbeats extension two computers make sure the other is still alive by sending data back and forth to each other. The client (user) sends its heartbeat to the server (website), and the server hands it right back. If by chance anyone of them goes down during the transaction, the other one will know using heartbeat sync mechanism.


When that heartbeat is sent, a small amount of the server’s short-term memory of about 64 kilobytes comes in reply from server and an attacker is supposed to grab it, that can leak sensitive data such as message contents, user credentials, session keys and server private keys. By sending heartbleed requests multiple times, an attacker is able to fetch more memory contents from the server.

This means, everything and anything in the memory such as SSL private keys, user keys used for your usernames and passwords, instant messages, emails and business critical documents and communication, and many more is vulnerable to cyber criminals. At this phase, you have to assume that it is all compromised.

About two-thirds of web servers rely on OpenSSL, means the information passing through hundreds of thousands of websites could be vulnerable.


So far, Security experts have found no direct evidence that anyone has managed to use the bug to steal information. The vulnerability has been fixed in OpenSSL v1.0.1g.


Major websites, including Gmail and YouTube, Facebook, Tumblr, Yahoo and Dropbox have fixed the problem, but there are still thousands of websites who are yet to fix the problem. Users are advised to change their passwords on only those affected websites, that tell you they've fixed the problem. READ MORE on how to protect yourself from Heartbleed bug.

Continue reading →

OpenSSL vulnerability allows hackers to read 64k of memory on target server

0 comments


HeartBleed: A potentially critical security vulnerability in OpenSSL has been discovered that allows an attacker to read up to 64kilobytes of memory from the server running a vulnerable OpenSSL version.

As a normal user, you may not aware what is OpenSSL.  It is cryptographic library which is used for encrypting communication between web server and users - used by plenty of websites including Google, Yahoo, Twitter.

The bug( CVE-2014-0160), dubbed as 'HeartBleed', was independently discovered by Neel Mehta from Google Security team and Codenomicon.  The bug appropriately named HeartBleed because vulnerability is located in HeartBeat extension and it leads to memory leak.

The attacker can read only up to 64k of memory during one iteration of the attack.  However, according to Heardbleed.com, an attacker can "keep reconnecting or during an active TLS connection keep requesting arbitrary number of 64 kilobyte chunks of memory content until enough secrets are revealed".

An attacker can retrieve the private key used for encrypting the communication that will allow to read all information passed to server and user like it wasn't encrypted at all.

How to fix it?
If your server is using OpenSSL 1.0.1 and 1.0.1f, then better upgrade to 1.0.1g. If you are using 1.0.0 and 0.9.8, you are not vulnerable to this bug.  As a temporary fix, users can remove HeartBeat extension by recompiling OpenSSL with -DOPENSSL_NO_HEARTBEATS

Check whether Your server is vulnerable or not:
"http://filippo.io/Heartbleed/" allows to find whether your server is vulnerable to this bug or not.

Details about the Bug:
TLS Heartbeat extension is to ping from one end to another end - a specific message with size of it is being sent from client to server and server responds with the same message.

But, if an attacker send a small size of data(Let's say 1 kilo byte) and claims it's large size(64k), then the server(running vulnerable OpenSSL) will respond with 1 kilo byte of attacker's data + 63 kilobytes of data read from memory of the server.

Technical details of this bug can be found here .(read only if you are good in 'C' program).

Here is POC script written in Python: https://gist.github.com/ixs/10116537

*Update:
Metasploit Module :
https://github.com/rapid7/metasploit-framework/blob/master/modules/auxiliary/scanner/ssl/openssl_heartbleed.rb

Nessus Plugin:
http://www.tenable.com/plugins/index.php?view=single&id=73404

Nmap Script(NSE):
http://nmap.org/nsedoc/scripts/ssl-heartbleed.html

One should always be careful, when using pointers in C programming ;)
Continue reading →

Ministry of Health Saudi Arabia website defaced by Moroccan hackers

0 comments


Moroccan Islamic Union-Mail hacks and deface the official website of prevention program of injuries and accidents - Ministry of Health Saudi Arabia(moh-ncd.gov.sa)

The site was showing a picture of Mohamed Morsi The President Of Egypt and member in the Muslim Brotherhood and a clear message in arabic which said :

"Penetration in response to a statement by the Ministry of Interior inclusion of the Muslim Brotherhood in the list of terrorist groups."

"Our message to the governor of Saudi Arabia: The day will come who are under it is exposed to more than what it is now Syria." hackers said.

" The most worthy AQIM contain the Two Holy Mosques to be a compromise in everything Do not be biased for a class to another, until he became Al Saud believe in all that is Islamic terrorist And all of the resistance for pursuing terrorism The injustice of kin most Reluctantly --- one of Hussam signed Mohannad. Signature: Moroccan Islamic Union-mail"

The mirror of the defacement is available here:  http://www.aljyyosh.org/mirror.php?id=125826

This is not the first time the site being targeted by hackers - Earlier this year, a hacker going by handle 'Dr.SHA6H' also defaced the website.


Continue reading →

Wednesday, 9 April 2014

Hackers Can Unlock Tesla Cars by Stealing Owners’ Passwords

1 comments
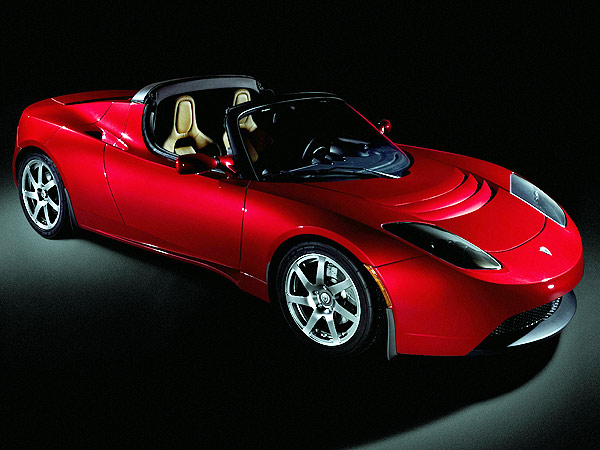
http://www.teslasociety.com/pictures/global_warming/tesla_roadster.jpg 


Corporate security consultant and Tesla owner Nitesh Dhanjani said that hackers can potentially unlock Tesla cars by stealing owner's password. Tesla cars are password protected. When a customer buys the car he will be required to obtain a password from Tesla's official website.
 The password that’s set by Tesla owners when they create an account is six characters long, and it must contain at least one number and one letter. This makes the password easy to obtain with brute-force attacks. Since it’s only 6 characters long, it’s not difficult to crack. 
Furthermore, there are no account lockout policies for incorrect login attempts. Nitesh Dhanjani says hackers can also employ certain other methods to obtain the password which may include phishing and social engineering. Nitesh said the if hackers get access to password they can lock and unlock the car can steal valuables placed inside. 
Hacker can also flash lights and can remotely locate the cars. Nitesh has submitted the findings to the company. Tesla assured that it will consider all possible risk and take the necessary measures accordingly.
Continue reading →

Hackers use security camera DVRs for bitcoin Mining

0 comments
 http://www.thestar.com.my/~/media/Images/TSOL/Photos-Upload/Technology/2013/12dec/03/bitcoinonline.ashx/?w=620&h=413&crop=1&

Security researchers at the SANS Institute's Internet Storm Center has reported that hackers are using DVRs, a device which receive and process images from security camera, as Bitcoin mining rigs. 

The malware is compiled for ARM CPUs, so it's a specialist nasty. They hackers have created a custom code which can be injected into DVRs. For this hackers will have to brute force or social engineer the passwords. 

In case of security cameras the password is usually easy can be brute forced with in short period. After getting administerative privileges, hackers will install a simple yet nasty malware on the host machine. 

This malware scans for vulnerable Synology Disk Stations as well as attempting tomine BitCoins. "The malware is an ARM binary, indicating that it is targeting devices, not your typical x86 Linux server," explains SANS Institute researcher Johannes Ullrich in a write-up . 

The malicious code is only scanning for vulnerable Synology Disk Stations and not doing anything on these insecure networks attached storage devices, at least for now.
Continue reading →

Hackers Target Al Arabiya, Leak Passwords After Exploiting Zimbra Vulnerability.

0 comments
http://www.debbieschlussel.com/archives/alarabiya2.jpg 

Hackers associated with notorious LullzCrew are back in public stunts. Yesterday they targeted Al Arabia, Saudi owned Tv Channel, and leaked its sensitive data. Lullz Crew says it's back again and now it has teamed up with Horsemen of Lullz, another hacktivist group, to launch a massive operation against the system. Lullz Crew had been in news for attacking largest media organization before. 

This time too, they have targeted Al Arabia, the leading media franchise in Middle East. The hackers wrote in a statement next to the data they leaked, " Al Arabiya is the second largest news agency in the Middle East. 

Considering we've been targeting large media corporations? Well, it falls right into our range; So, without further ado. NullCrew and The Horsement Of Lulz persent to you? The candies,” The hackers exploited the vulnerability in email and web client software Zimbra to gain access to data. LullzCrew told Softpedia that they have got access to a huge amount of data , “Do we plan to release more? It all depends on how much use it holds to us, things of particular use can be used over, and over again. We treat certain data the same way we treat 0day. Why leak it when it can be used properly down the road?” they told in a Twitter message.
Continue reading →

Monday, 7 April 2014

WinRAR File Extension Spoofing vulnerability allows Hackers to Hide Malware

0 comments

WinRAR file extension spoofing vulnerability


Imagine, You Open a Winrar archive of MP3 files, but what if it will install a malware into your system when you play anyone of them.


WinRAR, a widely used file archiver and data compression utility helps hackers to distribute malicious code. Israeli security researcher Danor Cohen (An7i) discovered the WinRAR file extension spoofing vulnerability.

WinRAR file extension spoofing vulnerability allows hackers to modify the filename and extension inside the traditional file archive, that helps them to hide binary malicious code inside an archive, pretending itself as '.jpg' , '.txt' or any other format.Using a Hex editor tool, he analysed a ZIP file and noticed that winrar tool also adds some custom properties to an archive, including two names - First name is the original filename (FAX.png) and second name is the filename (FAX.png) that will appear at the WINRAR GUI window.Danor manipulated the second filename and extension to prepare a special ZIP archive, that actually include a malware file "FAX.exe", but displaying itself as "FAX.png" to the user.WinRAR file extension spoofing vulnerabilityCyber intelligence company, IntelCrawler also published a report, which revealed that cybercriminals specialized in cyber espionage attacks are using this zero-day vulnerability in the wild to target several aerospace corporations, military subcontractors, embassies, as well as Fortune Global 500 companies.Using this technique, an attacker can drop any malware in very convincing manner to the victim's system. "Using this method the bad actors bypass some specific security measures including e-mail server’s antivirus systems" IntelCrawler said.Danor successfully exploited winrar version 4.20, and IntelCrawler confirmed that the vulnerability also works on all WinRar versions including v.5.1.

HOW TO CREATE EXPLOITABLE ZIP FILE?
A video demonstration has been prepared by Indian Security Researcher Ajin Abraham, shown below:
"One of the chosen tactics includes malicious fake CV distribution and FOUO (For Official Use Only)-like documents, including fax scanned messages"

Using social engineering techniques, attacker are targeting high profile victims with spear phishing mails, "Most of sent malicious attachments are hidden as graphical files, but password protected in order to avoid antivirus or IDS/IPS detection." IntelCrawler reported.
WinRAR file extension spoofing vulnerabilityIn above example, the Malware archive file was password protected to avoid antivirus detection, used in an ongoing targeted cyber espionage campaign.

Researchers found Zeus-like Trojan as an attachment, which has ability to establish remote administration channel with the infected victim, gather passwords and system information, then send the collected and stolen data to the Command & Control server hosted in Turkey (IP 185.9.159.211, Salay Telekomünikasyon).


Users are advised to use an alternative archiving software and avoid opening archives with passwords even if it has legitimate files.

Continue reading →

BJP Junagadh website hacked by Pakistani hackers

0 comments

Local news organizations reports that BJP Junagadh unit's website (bjpjunagadh.org) was hacked and defaced by some unknown hackers.

The hackers who defaced the website posted comments against BJP and RSS. The defacement also contains several images of people burning and standing on the Indian tricolor.

We have referred some defacement-mirror websites, the hack appears to have taken place in February.  It is unclear whether these local reports referring this incident or the website got defaced again today.

According to the defacement-mirror record(hxxp://dark-h.org/deface/id/12604), this website was defaced by a Pakistani hacker going by handle "Sniper haxXx" who is responsible for many Indian websites' hacks.

"As soon as I reached office, our IT cell employees told me that someone has hacked our website http://www.bjpjunagadh.org and uploaded photographs and comments to malign reputation of BJP, RSS and Narendra Modi,"Indian Express quoted In-charge of BJP Junagadh office Raju Jivani as saying.

A complaint has reportedly been lodged against the unknown hacker, police are trying to find the hacker who is responsible for the breach.

Meanwhile, Gujarat Pradesh Congress Committee's President Arjun Modhwadia told reporters that "This is purely an attempt to get votes by playing the communal card ahead of the election"
Continue reading →

WinRAR File Extension Spoofing helps Hackers to Hide Malwares

0 comments

WinRAR , a tool which is mostly used by 90% of the people around the world to compress files or to extract ZIP files which are already compressed. WinRAR is even the most famous and much popular than other tools which compress or extract ZIP files.

Imagine that you opened a RAR file which had some images or some mp3 music files but when you played or opened any single of them , it installed a malware on your system. Wouldn't that be dangerous ? Yes ! obviously it will be ! This file extension spoofing vulnerability was discovered by a Israeli security researcher Danor Cohen (An7i). 


The WinRAR File Extension Spoofing was done by an Israeli security researcher , he used a hex editor in which he noted that WinRAR adds two things in an archive file , it adds first name and second name of file. First name of the file contains the name of the original file and the second name contains the file name with extension which shows in WinRAR GUI window. Danor Cohen just edited the second name to "FAX.png" as the original malware name and extension was "FAX.exe".

This helped him to get victims trapped easily as when they open any format file which is shown in WinRAR GUI window , it shows some other file extension but it runs a malware with .EXE extension and the attacker successfully gets access to the victims computer.
Continue reading →

Two Hackers Plead Guilty in $15 Million Cybercrime Operation

0 comments


Two American hackers have admitted to have stolen some $15 million, before a New Jersey court, authorities say. Robert Dubuc, 40, of Malden, Massachusetts, and Oleg Pidtergerya, 49, of Brooklyn, New York, pleaded guilty to wire fraud conspiracy, conspiracy to commit access device fraud and identity theft before U.S. District Judge Peter Sheridan in Trenton federal court. 

U.S. Attorney Paul Fishman in a statement said that both the men had been involved in a campaign to "cash out" bank accounts and pre-paid debit cards opened in the names of others. 

He said The hackers tapped into accounts in 2012 and 2013 at global financial businesses and institutions - Citibank N.A., JP Morgan Chase Bank N.A., PayPal, TD Ameritrade, the U.S. Department of Defense, TIAA-CREF and others - and diverted money to accounts and debit cards they controlled, Fishman said. They then employed "cash out" operations, using people who would withdraw the stolen funds at ATMs and with fraudulent purchases in New York, Massachusetts, Illinois, Georgia and elsewhere. 

Wire fraud conspiracy carries a potential sentence of 20 years in prison, while the other two charges each carry the possibility of five years in prison, as well as heavy fines. 

Sentencing was scheduled for July 7 for Pidtergerya and July 8 for Dubuc. The investigation was carried out by US Federal Agencies.
Continue reading →

Sunday, 30 March 2014

Arab Hackers Breach Israeli Cyberspace and Threaten Israeli Journalists.

0 comments
 http://davidshoebridge.org.au/wp-content/uploads/2013/05/Shrinking-Palestine-1024x724.jpg

Recently, Muslim hackers breached Israeli cyberspace and comprised www.israeldefense.com. Following this attack, hundreds of Israeli citizen and journalists have been receiving threatening text sms warning them of grave consequences and possible retaliation if Israel continues in occupying Gaza.


 Time of Israel has been tracing the activity and suggests that the hundreds phone numbers of citizens and journalists who are receiving SMS had been stolen when Israeli defense forum was compromised last month. Some of text msgs received by Israeli reads as follows: " ‘revenge’, “a warning to the Zionists, the al-Qassam rockets are waiting for you”, “Al-Qassam has chosen you to be the next Shalite (sic),” a reference to Gilad Shalit, an Israeli soldier kidnapped by Palestinians.
The message below the photo caption read: Ten years ago, Ismail Ahmed Yassin, our leader, was killed by three missiles as he left a mosque after morning prayers. This is a reminder that we do not forget our Sheikh’s blood on your hands. We vow once again that we will take revenge, and cut off the heads of your commanders.”


They gave stern warnings:
"Missiles killed our Sheikh and now, our missiles will hit every place in the State of Israel. Know that the next war will see the end of your country.” Furthermore, hacked email address of Israel's defense fourm is also sending threating emails to its subscribers. So far Israeli cyber security agencies have been unable to stop these sms.
Continue reading →

Exclusive : its not only Hackers , Journalists are also targeting other journalists

0 comments


Watch out Journalists! Some journalists are after you.
 C-net article by Don Reisinger , " Watch out, journalists: Hackers are after you claims many of the journalist-turned hackers are spying on other journalists to steal reports and classified information of their media outlet. 
Report is followed Google research which claimed that hackers are increasing targeting journalist to steal sensitive information. However its not just hackers who are behind journalists, but some Journalists are also behind other journalists. 
The revelation was made at the Black Hat Conference convenrd at Singapore in which three French journalists were expelled after they were accused of spy on the journalists' email accounts. All of these three French journalists work for the French publication Global Security Magazine. 


The French journalists captured what they claimed were usernames and passwords of reporters from at least two media outlets — eWeek and CNET News, according to that March 28, 2014 article, " Watch out, journalists: Hackers are after you ."
 The eWeek reporter told organizers his login credentials looked like they were legitimate, while the CNET information appeared to be bogus, the C- Net article reported. Black Hat attendees are warned that the conference's public wireless network is being monitored by hackers. This is most shocking to have surfaced so far about online security.
 For the first time WhoGotHacked has come to learn that its not just hackers who target journalists, but Journalists are also targeting other journalists and their personal information. The fact will greatly undermine the credibility of journalism and media franchise around the world.

Continue reading →

Hacker's Dome - Gamification the Information Security

0 comments
When it comes to Information Security, there's a great way to learn, train and keep sharp your skills. This can be done using gamification mechanics to speed up the learning curve and improve retention rate. Capture The Flag competitions use gamification mechanics and represent one of the best ways to learn security hands on.

The Infosec team behind Capture The Flag platform CTF365 has created a place for hackers to play weekend CTFs with great prizes, called Hacker's Dome. In order to access the Hacker's Dome, you need is a registered and confirmed CTF365 account. 

At Hacker's Dome CTF Platform users can deploy their own CTFs and can invite web developers, system administrators and security professionals to take hard challenges. Think RackSpace, of CTF Competitions. Hacker's Dome - First Blood: First Blood is the first CTF and will start on May 17 2014 15:00 UTC and winners will win more than $6000 in prizes.

If Information Security gamification got your attention, then all you have to do is to get your Hacker's Dome Access and prepare for First Blood CTF. 


1-Year Metasploit Pro for Everyone: All Hacker's Dome competition participants will get 'Full Year Metasploit Pro License'  as Raffle King Prize. "The fact that Metasploit gave us the opportunity to run a raffle off such great King Prize, makes us proud of what we've done and it encourages us to keep up our good work." team said.
Give it a try! Registrations are open for Hacker's Dome and it could become your weekend IT Security trainer - where fun, entertainment and awesome prizes will be at its best. Stay secure while having fun.Follow me on Google+, Twitter or Contact via Email.

View the original article here

Continue reading →

Over 20Gbps DDoS attacks now become common for Hackers

0 comments
Over 20Gbps DDoS attacks now become common for HackersThe Distributed Denial of Service (DDoS) attack has become more sophisticated and complex and therefore has become one of favorite weapon for the cyber criminals to temporarily suspend the services of any host connected to the Internet and till now nearly every big site had been a victim of this attack, from WordPress to online game websites.According to the new report released by a US based security solutions provider Incapsula, DDOS activities have become threefold since the start of the year 2013, pointing the key source of trash traffic to be the remotely controlled “zombie army” that can be used to flood various websites for DDoS attacks and other malicious activities.The report site as “DDOS Threat Landscape”, explains that almost one in every three DDoS attacks is above 20Gbps and 81% of attacks feature multiple vector threats.

The attackers are becoming more skillful at working around the network security and reusing their DDOS Botnets to attack multiple targets i.e. around 30% of the Botnets are flooding more than 50 targets a month.
“As early as February 2013 we were able to track down a single-source 4Gbps attacking server, which – if amplified – could alone have generated over 200Gbps in attack traffic,” the company said in its report.
Over 20Gbps DDoS attacks now become common for Hackers
“With such available resources it is easy to explain the uptick in attack volume we saw over the course of the year.”

Attackers are widely using two types of SYN flood attacks, i.e. regular SYN packets and large SYN packets. According to the report, 75% of all large scale network DDoS attacks that are peaking above 20Gbps are using both types of SYN flooding at same time.

However, currently amplification attacks became the most commonly used attack vector for large scale network DDoS attacks. During January and February of 2014 a significant increase in the number of NTP Amplification attacks was noted and Some statistics are also revealed an evolution of Application DDOS attacks, DDOS traffic is up by 240%, "in almost 30% of all recorded sessions, the DDoS bots Incapsula encountered were able to accept and store cookies, while 0.8% of these bots could also execute JavaScript."Over 20Gbps DDoS attacks now become common for HackersIn terms of emerging threats, the report titled “hit-and-run” DDoS attacks, which were first documented in April 2013 and are the part of another parallel trend of attacks that were specifically designed to exploit vulnerabilities in DDoS protection services and human IT operators.“These attacks, which rely on frequent short bursts of traffic, are specifically designed to exploit the weakness of services that were designed for manual triggering (e.g., GRE tunneling to DNS re-routing),” report reads. “Hit-and-run attacks are now changing the face of anti-DDoS industry, pushing it towards always-on integrated solutions.”Over 20Gbps DDoS attacks now become common for HackersAround one-third of all Botnets are located in India, China and Iran. The report ranks the United States as number five in the list of ‘Top 10’ attacking countries.

In order to infiltrate systems bots are using spoofed user-agents, which help them to bypass low-level filtering solutions and about 46% of spoofed user-agents came from Chinese search engine Baidu, while nearly 12% mimicked Google.

Continue reading →

Saturday, 29 March 2014

United States Of America Indicted 3 Hackers

0 comments

Three people were charged with getting involved in an worldwide cyber crime ring,which attempted to steal over $15 million by hacking into American customer accounts at 14 banking institutions along with the Department of Protection payroll service. These folks happen to be indicted through the U . s . States.

Two Ukrainians, Oleksiy Sharapka, 33, and Leonid Yanovitsky, 39, along with a US citizen, Richard Gundersen, 47, were indicted through the U . s . States on charges of conspiracy to commit wire fraud, conspiracy to commit access device fraud and id theft, and irritated id theft. Initially there have been eight people billed, but one of these was removed of billed and also the other four either pleaded responsible for still face them.

US Attorney described the gang compromised into accounts hold through the clients of numerous banking institutions, including Citibank, PayPal, E*Trade, JP Morgan Chase Bank, Nordstrom Bank, USA, and much more leading services. Their email list even includes the Defense Departments finance and accounting service.

The United States court will hear the way the trio acquired unauthorized use of systems and diverted customer funds to accounts and pre-compensated an atm card. Apparently, they employedcashers to create ATM distributions and pretend purchases in a number of US states. Following this, the people from the gang used stolen details to file for false tax statements and stated for refunds using the Irs.

The scam went for over a year  from 2012, when Sharapka was deported after serving over seven years in america prison, to the center of 2013. Based on prosecutors,Sharapka went the conspiracy with the aid of Yanovitsky, while Gundersen assisted them move fraud proceeds. Each hacker faces as much as two decades of incarceration around the wire fraud conspiracy count only.

As the Ukrainian accused havent been taken yet, the united states hacker was likely to answer the charge in the court later. Meanwhile, charges against another defendant, Ilya Ostapyuk, were ignored a couple of several weeks ago, based on court public records. For another 4 accused, they either pleaded guilty or still face charges.
Continue reading →
 
Copyright © 2013 MyBloggerBlog Template All Right Reserved
Designed by MyBloggerBlog | Powered by Blogger